

Identity Security
Most breaches don't break in. They log in. Identity Security covers the modern identity attack surface: identity threat detection and response (ITDR), business email compromise, Microsoft 365 compromise, OAuth attacks, credential theft, MFA gaps, and rogue app detection. Learn about both the threats and the Huntress capabilities built to stop them.
The Latest Identity Security Blog Posts

Unboxing Phishing Kits: Advanced Cred Theft for Entry-Level Hackers
Unboxing Phishing Kits: Advanced Cred Theft for Entry-Level Hackers
Oct 22, 2026
M365 Token Spray and Replay Campaign Compromises Business Email Accounts
M365 Token Spray and Replay Campaign Compromises Business Email Accounts
Oct 22, 2026
Introducing ITDR Lookback: Find Out Who Was in Your Microsoft 365 Tenant Before You Were
Introducing ITDR Lookback: Find Out Who Was in Your Microsoft 365 Tenant Before You Were
Oct 20, 2026
ConnectWise (SkyKick) Vendor Credentials Abused in M365 Attacks

ConnectWise (SkyKick) Vendor Credentials Abused in M365 Attacks
Oct 16, 2026
Passkeys Raise the Bar. Here’s Where Attackers Can Still Get In.
Passkeys Raise the Bar. Here’s Where Attackers Can Still Get In.
Oct 14, 2026
Fully Managed or Modified: Pick How Huntress Hardens Your Microsoft 365 Environment with Managed ISPM
Fully Managed or Modified: Pick How Huntress Hardens Your Microsoft 365 Environment with Managed ISPM
Sep 24, 2026
Stealing OAuth Tokens Through Microsoft's Front Door
Stealing OAuth Tokens Through Microsoft's Front Door
Sep 23, 2026
Inside Knight Office, a New M365 AiTM Phishing Kit
Inside Knight Office, a New M365 AiTM Phishing Kit
Sep 2, 2026
The New Huntress Managed ITDR Dashboard: More Context. Faster Answers.
The New Huntress Managed ITDR Dashboard: More Context. Faster Answers.
Aug 27, 2026
No (Bad) CAP: Inside an Ongoing LSHIY Password Spray Attack
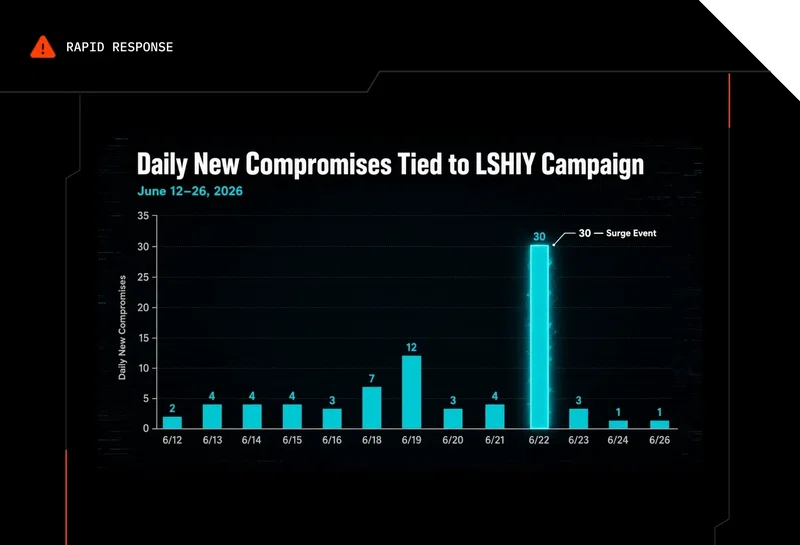
No (Bad) CAP: Inside an Ongoing LSHIY Password Spray Attack
Jun 30, 2026
Hook, Line, and Token: Anatomy of the Kali365 / Octopi365 Phishing-as-a-Service Kit
Hook, Line, and Token: Anatomy of the Kali365 / Octopi365 Phishing-as-a-Service Kit
Jun 11, 2026
dMSA Ouroboros: Self-Sustaining Credential Extraction in Windows Server 2025
dMSA Ouroboros: Self-Sustaining Credential Extraction in Windows Server 2025
A fully patched Windows Server 2025 domain is vulnerable to dMSA Ouroboros—a self-sustaining credential extraction technique requiring only standard delegated permissions. Learn how it works, why remediation fails, and how to detect it.
May 4, 2026
