


Cybersecurity 101
What is a Security Email?
Learn what a security email is, how it protects against cyber threats, and why it’s essential for cybersecurity. Beginner-friendly insights from Huntress.
Privileged Access Management Best Practices for Lean IT Teams
Privileged Access Management Best Practices for Lean IT Teams
You’re probably already doing privileged access management. You just don’t call it that.
It’s the shared admin password spreadsheet someone started three years ago. It’s a quick look at who’s in the Domain Admins group before an audit. No platform. No dedicated team. Just you, keeping the keys safe by hand.
That’s a real start. Here’s how to tighten it up without buying anything first.
Privileged Access Management is a comprehensive set of strategies and technologies designed to manage and secure accounts with elevated permissions. Its primary goal is to enforce the principle of least privilege, ensuring users only have the minimum access necessary for the shortest time required.
Privileged accounts (such as Domain/Local Admin, Service, and Emergency/Break-Glass accounts) possess permissions beyond standard users. Because they can change system configurations and access sensitive data, they represent the highest risk if compromised.
A modern PAM approach focuses on on-demand provisioning. Rather than having permanent "standing" administrative rights, users are granted temporary elevation only when a specific task requires it, after which access is automatically revoked.
Beyond security, PAM improves operational efficiency by automating password management and rotation, and ensures regulatory compliance (CMMC,GDPR, HIPAA, PCI DSS) by providing unalterable audit trails
Privileged access management (PAM) is the set of practices that control, limit, and monitor who can use elevated permissions in your environment. It’s a discipline first and a product second, so PAM software can help, but you can start without it.
PAM starts with knowing which accounts carry the most power. For most lean teams, three matter most:
Application accounts carry the same risk as service accounts. Elevated human accounts are just administrator accounts assigned to one person.
A single compromised admin account can let an attacker move laterally across your network within minutes of a breach. That’s why privileged accounts are the number one target in identity-based attacks. Every unused admin right widens your attack surface, whether the threat is a disgruntled employee or or an outside attacker taking advantage of a misconfigured cloud (our cloud security best practices cover how to avoid that). Over-privileged accounts are the easiest way in.
Benefit | The risk it closes |
Enhanced security | Credential theft and lateral movement. Limiting what each privileged account can reach means one stolen password doesn’t turn into a full network takeover. |
Regulatory compliance | Failed audits. Auditors want proof of who accessed what, and when. Standing privileges can’t show that, because the access is always on. Time-bound, logged access can. |
Improved accountability | Shared logins that hide who did what. Privileged session logging ties every action to a named person, so “who changed that?” takes minutes to answer. |
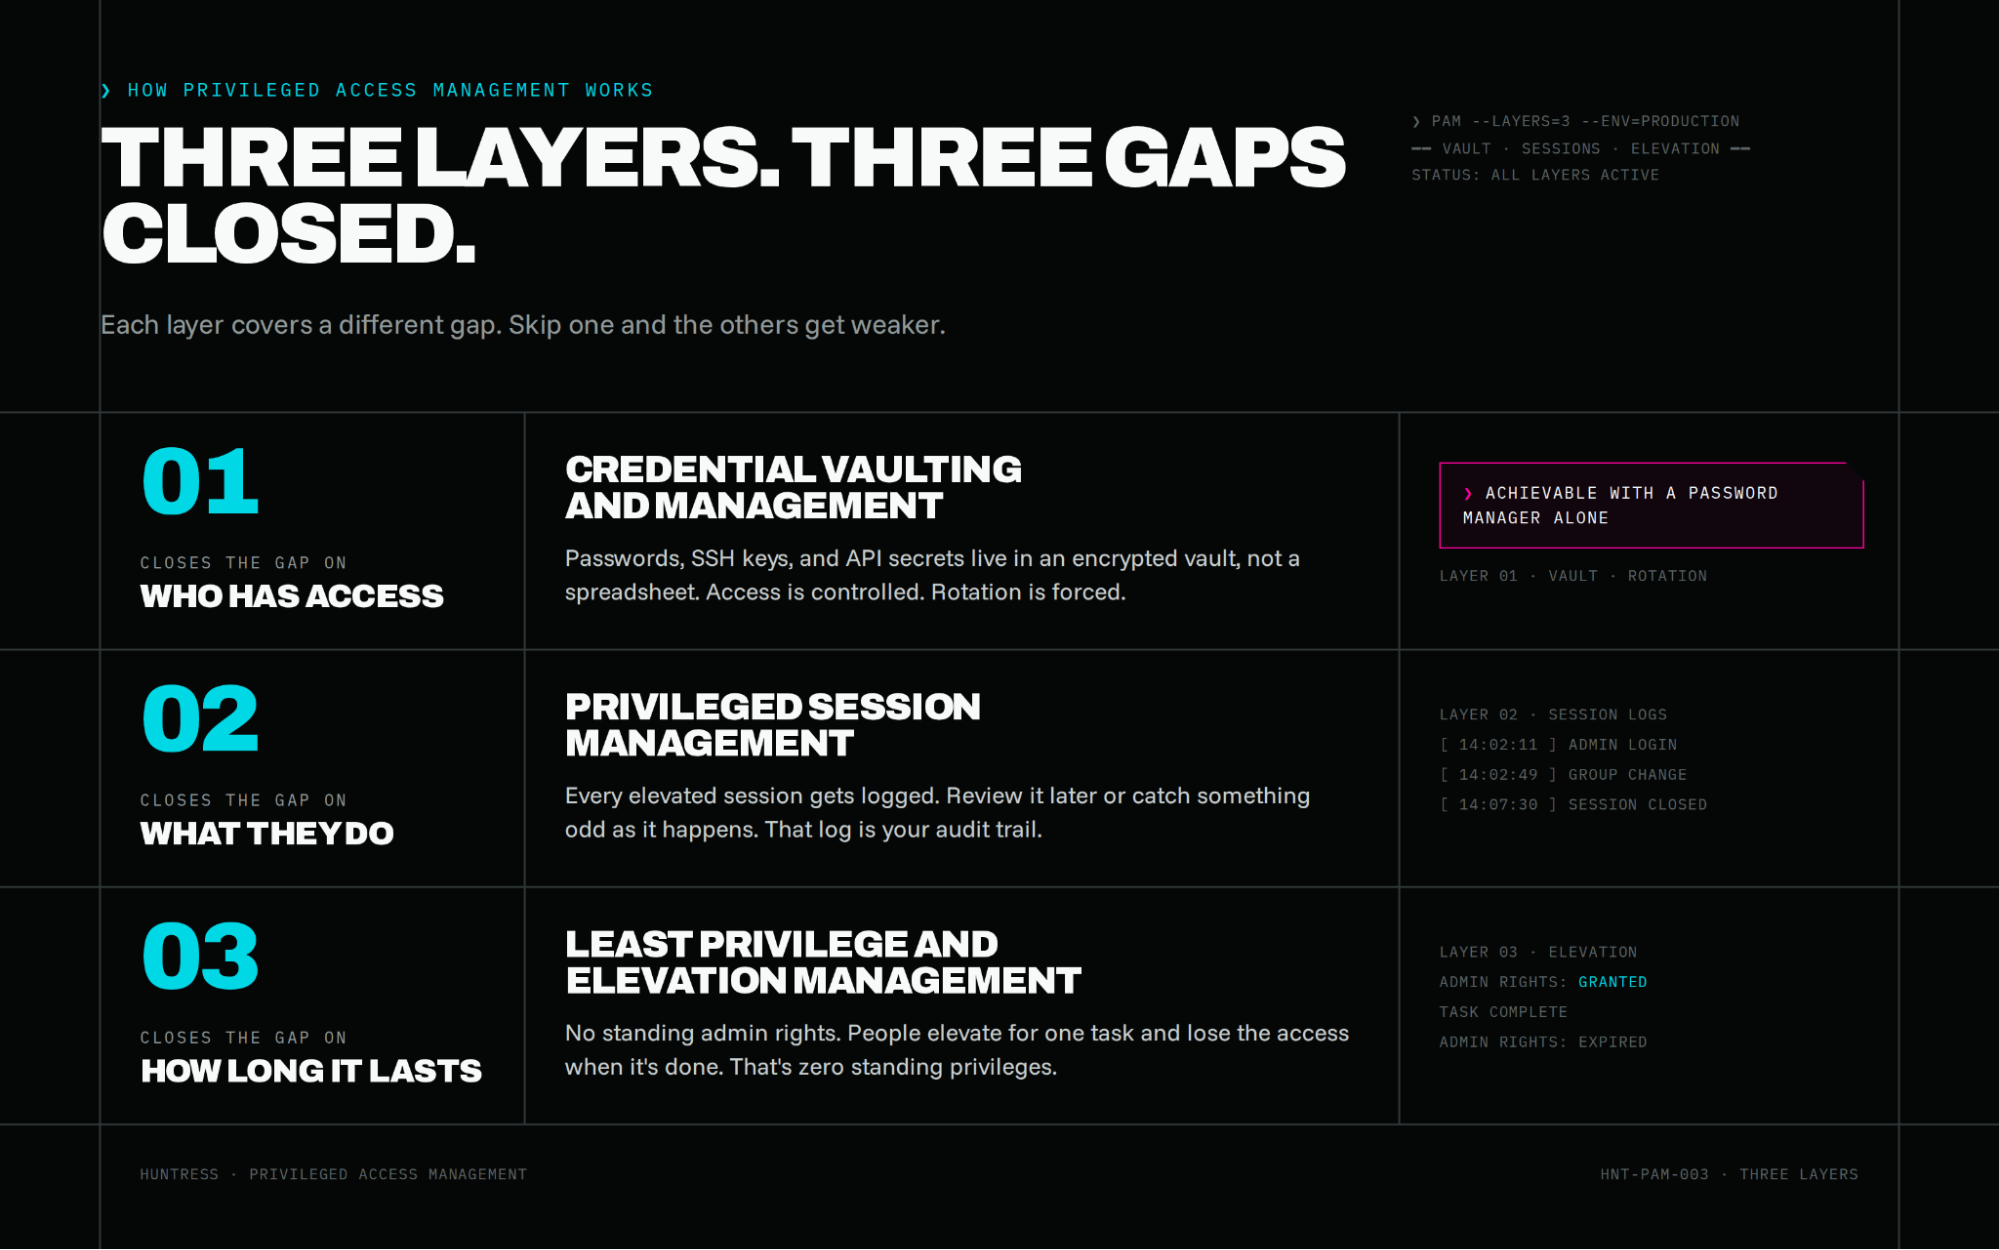
PAM works in layers, and each layer closes a different gap: who has access, what they do during that access, and how long it lasts. Skip one and the others get weaker.
Credential vaulting stores passwords, SSH keys, and API secrets in an encrypted vault instead of a spreadsheet. Access is controlled, rotation is forced, and nobody’s emailing a password. A password manager can handle this layer on its own.
Privileged session management tracks what happens after someone logs in with elevated rights. Logged sessions let you review activity later or catch something odd as it happens. That log is your audit trail.
This layer answers “how long?” Instead of standing admin rights, people elevate for a specific task and lose the access when it’s done. That’s the idea behind zero standing privileges, and it shrinks the window an attacker can use.
The six PAM best practices are inventorying accounts, vaulting credentials, enforcing least privilege and just-in-time access, isolating and monitoring sessions, securing credentials, and watching for privilege escalation. You don’t need to buy a dedicated PAM platform first to start any of them.
Practice | With a dedicated PAM platform | Without one (native tools) |
Inventory all privileged accounts | Automated account discovery across systems | A quarterly manual audit of Active Directory admin groups |
Vault all privileged credentials | Built-in vault with automated rotation | A password manager with shared, access-controlled vaults and forced rotation |
Implement least privilege and JIT access | Approval-based, automated elevation | Time-bound Active Directory group membership, removed manually or by a scheduled task |
Isolate and monitor privileged sessions | Built-in session recording | Native Windows Event Log auditing forwarded to a SIEM |
Secure privileged credentials without a dedicated platform | Vendor-hardened vault and isolation | An Active Directory Tier 0 model isolating admin accounts |
Watch for privilege escalation | Built-in alerts on privilege changes | An alert on changes to privileged group membership |
Vaults and policies close doors. They don’t tell you when someone’s walking through one.
See how Huntress Managed ITDR protects privileged accounts, or start your free Huntress trial.
Most PAM-related breaches don’t come from a missing tool. They come from a privileged account nobody was watching.
When you’re ready to compare vendors, the Practical ITDR Buyer’s Guide shows you what to ask.
Domain and local administrator accounts, shared and service accounts, and emergency break-glass accounts. Application accounts and elevated human accounts count too.
A password manager covers vaulting, one layer of PAM. PAM also covers session oversight and limiting how long elevated access lasts.
Attackers go after privileged accounts first because one compromise opens everything else. Growing businesses often have more standing admin rights than they realize, and fewer people watching them.
No. The “without one” column in the best practices table shows how to cover each practice with tools you likely already have: a password manager, Active Directory, and native logging. A platform adds automation as you grow, but it isn’t the starting line.
Additional Resources
Learn what a security email is, how it protects against cyber threats, and why it’s essential for cybersecurity. Beginner-friendly insights from Huntress.

Learn what dump data is, why cybercriminals target it, and how to protect your database dumps from security threats. Essential guide for IT professionals.

Learn what security directors do, their evolving role in cybersecurity, required qualifications, and career opportunities in this comprehensive guide.

