Rapid Response & Vulnerabilities
When a vulnerability starts getting exploited, the clock starts. Rapid Response & Vulnerabilities covers CVE disclosures, vulnerability advisories, the exploitation activity we see in the wild, patch guidance, and disclosure timelines. Timely, focused, and built around what to do next.


The Latest Rapid Response & Vulnerabilities Blog Posts


Rapid Response: php2shell, Leaked Critical PHP Vulnerabilities (CVE-2026-109618 & CVE-2026-109619)
Threat Actors Exploit Critical AhsayCBS Flaws to Drop Webshells and XMRig Cryptominer
Rapid Response: Critical N-able N-central Vulnerability and Active Exploitation
PaperCut Actively Exploited: A Pre-Auth RCE Chain
Seven Steps to Ransomware: CitrixBleed 2 Weaponized by Initial Access Brokers
Cybercrime Breaches Klue: Salesforce Data Impacted for Many Victims, including Huntress
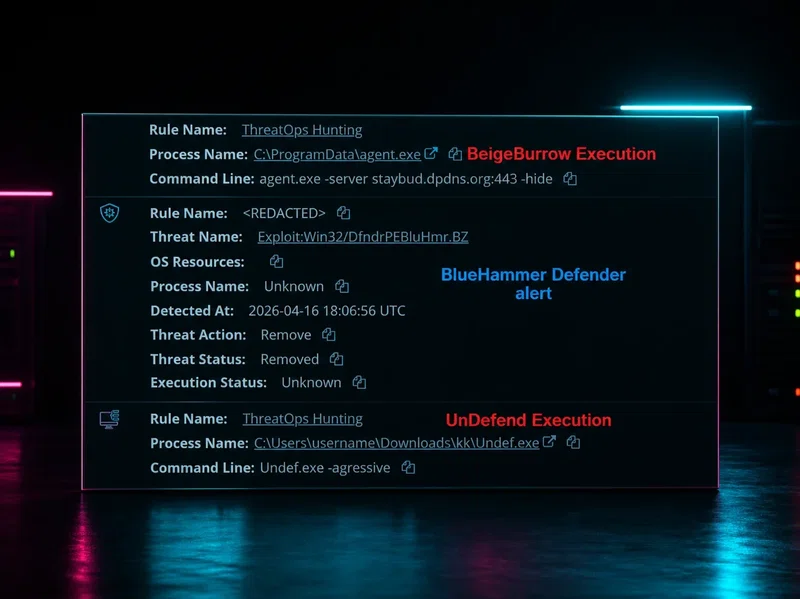
Nightmare-Eclipse Tooling Moves From Public PoC to Real-World Intrusion
Huntress observed in-the-wild use of Nightmare-Eclipse tooling, including BlueHammer, RedSun, and UnDefend, in a live intrusion involving FortiGate VPN compromise as the initial access, reconnaissance commands, and likely tunneling activity.
Supply Chain Compromise of axios npm Package
Active Exploitation of SolarWinds Web Help Desk
Huntress observed active exploitation of SolarWinds Web Help Desk across three customers — with attackers deploying Cloudflare tunnels and Velociraptor for persistence immediately after getting in.
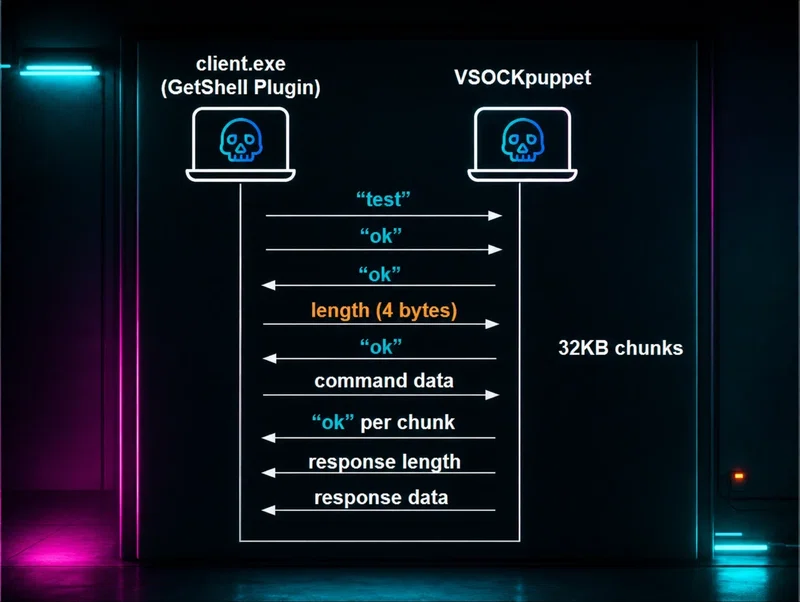
The Great VM Escape: ESXi Exploitation in the Wild
An ESXi VM escape exploit appeared in the wild with simplified Chinese development paths and the characteristics of a zero-day. Huntress traced the intrusion from SonicWall VPN all the way through.
Active Exploitation of Gladinet CentreStack/Triofox Insecure Cryptography Vulnerability
Gladinet CentreStack is being actively exploited, with the cl0p ransomware group now reportedly targeting internet-facing servers. Huntress has been tracking this from the start and has the latest updates.