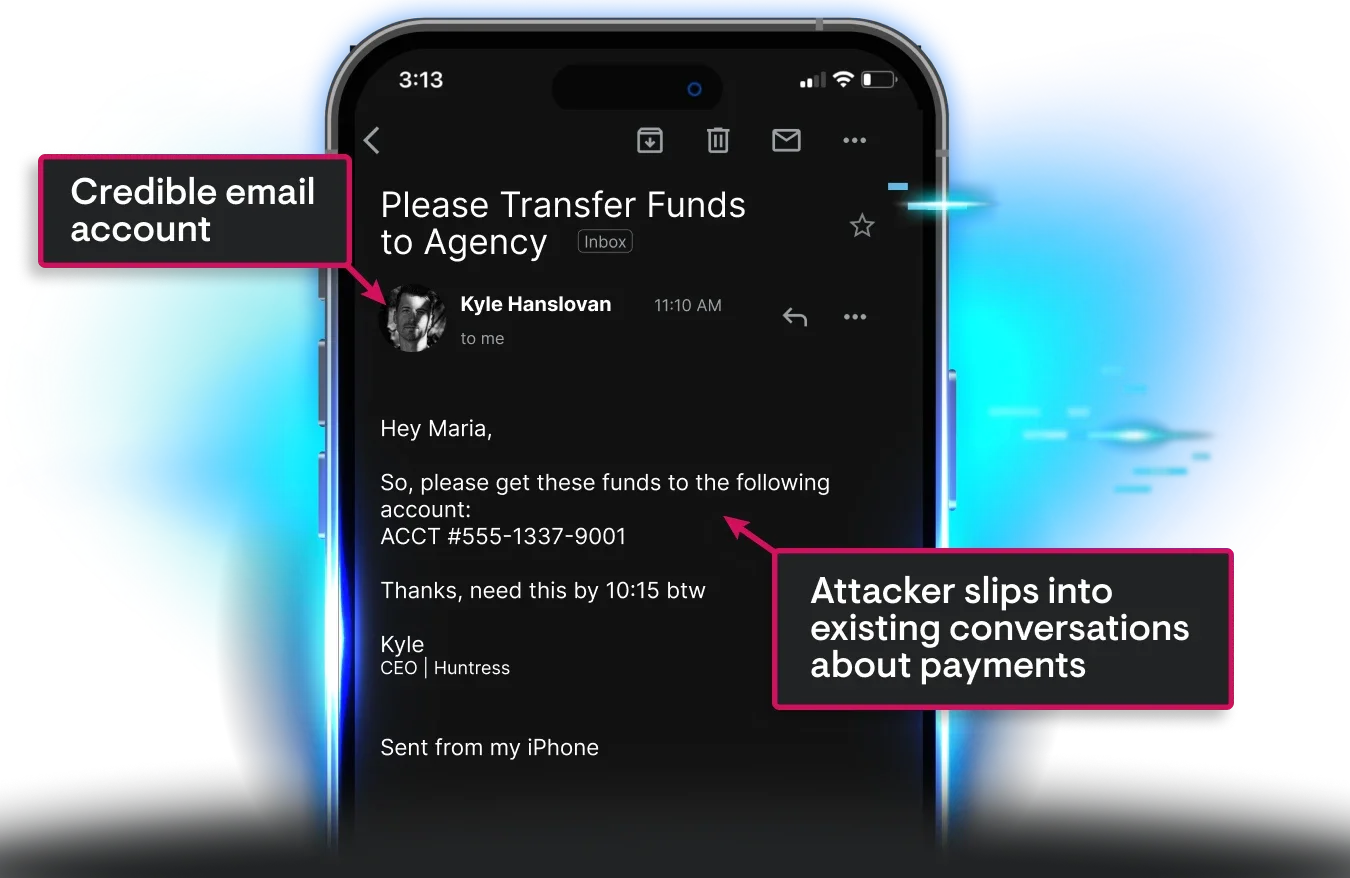
An incident responder is a cybersecurity professional who detects, investigates, and manages the aftermath of cyber incidents to limit damage and get systems back up and running.
Simply put, incident responders jump into action when security alerts hit, figure out what happened, and help organizations contain and recover from threats like hacks, ransomware, or data breaches.
If you want to know what actually happens when “something bad” is detected in a company’s network, then you may be interested in learning more about what an incident responder does on a day-to-day basis.
What is an incident responder?
At its core, an incident responder is like the emergency team for digital disasters. When a cyber threat hits, incident responders step in to identify what happened, contain the spread, and help the business recover as fast (and painlessly) as possible.
They’re pros at handling surprises—from mysterious malware to high-stakes ransomware attacks. Their mission: stay calm under pressure, make sense of digital chaos, and protect an organization’s systems, data, and reputation.
You’ll find incident responders in all sorts of workplaces, from big banks to government agencies and small IT teams. Some work full-time inside security operations centers (SOCs), while others are called in as experts when things go sideways.
Main tasks and responsibilities
Incident responders rock a job that combines detective work, communication, and technical know-how. Here’s what they handle, day in and day out
Investigation: Collect clues (log files, emails, etc.), analyze what happened, and trace the root cause of incidents.
Containment and eradication: Move fast to stop attackers, block suspicious users or devices, and scrub systems of malware.
Recovery: Help restore affected systems, ensuring everything is clean and safe to use again. This often means working with IT to reinstall software, recover data, or change passwords.
Documentation: Write detailed reports on what happened, what actions were taken, and recommendations for closing gaps.
Communication: Coordinate with other teams and, in some incidents, notify management or law enforcement.
Why is incident response critical in cybersecurity
Incident response isn’t just “nice to have.” Without it, even small cyber incidents can spiral into full-blown disasters, costing companies money, reputation, and customer trust.
Cyber threats are a daily reality: Cyber attacks like phishing, malware, and ransomware can hit any organization at any time.
Regulations demand action: Industries like healthcare, finance, and energy are required by law to report breaches and have response plans in place.
Speed matters: The faster an attack is contained, the less damage it can cause.
Incident responders are the heroes who make sure security incidents are managed quickly and efficiently, limiting their impact on the business and (sometimes) stopping attackers in their tracks.
What skills do incident responders nee?
It’s not just about tech savvy. Here’s what great incident responders bring to the table
Technical skills
Deep understanding of computer networks, operating systems, and common cyberattacks.
Experience with forensic analysis tools and SIEM systems.
Ability to analyze logs, malware, and suspicious behavior.
Soft skills
Resilience under pressure. Incidents often mean high-stress, high-stakes situations.
Communication. Explaining complex issues clearly to both technical teams and management.
Attention to detail. Small clues are often critical for resolving incidents.
Incident responders are cyber emergency responders, handling everything from detection to recovery. This role is critical for reducing the business, data, and reputation damage caused by cyber incidents. With new attacks happening daily, skilled incident responders are more in demand than ever. Starting out means focusing on IT basics, hands-on skills, and relevant certifications.
The job isn’t just technical—communication, teamwork, and a cool head are must-haves.
They investigate security alerts, contain or eradicate attacks, document what happened, and help restore affected systems. They’re first on the scene when something suspicious pops up in the network.
Not usually. While a basic understanding of scripting (like Python, PowerShell, or Bash) can help, strong IT system knowledge and investigative skills matter more.
Incident responders focus on actively handling security events as they happen, rather than just building or maintaining defenses. They’re the fire brigade for cyber emergencies.
Certs like GIAC Incident Handler (GCIH), CompTIA CySA+, and SANS CSIR are great starting points. They prove you know how to detect, analyze, and respond to threats.
Absolutely! Many work from home, especially if their organization uses cloud-based security tools. Some situations (like hands-on system fixes) might require on-site work.
Fraudulent Wire Transfers: How Can Businesses Prevent Them?
Fraudulent wire transfers are nearly impossible to reverse. Learn how business email compromise enables wire fraud and how Huntress Managed ITDR prevents attacks.
Proactive Cybersecurity Solutions for SMBs and MSPs
Protect your business from PoC-based threats with Huntress. Discover our people-powered cybersecurity solutions that hunt, analyze, and respond before exploits strike.
What Is Conti? Understanding Conti Ransomware & Its Spread
Learn about Conti Ransomware, how it spreads, and its impact on cybersecurity. See key takeaways for protecting against this prominent ransomware threat.
What Is Data Encryption? Why It Matters for Security
Learn how data encryption protects sensitive information using algorithms and keys. Discover encryption types, best practices, and compliance requirements.
Learn about MTAN (Mobile Transaction Authentication Number) and its role in secure online transactions. Understand how it protects against cyber threats.
Protect What Matters
Secure endpoints, email, and employees with the power of our 24/7 SOC. Try Huntress for free and deploy in minutes to start fighting threats.