Huntress Managed SIEM

Your Security Tools See Events. SIEM Sees the Attack.

Huntress Managed SIEM

Your Security Tools See Events. SIEM Sees the Attack.

Your security tools are watching. But who’s connecting the dots?


Attackers don’t operate in silos, and your security shouldn’t either. Huntress Managed SIEM connects activity across endpoints, identities, networks, and cloud services to uncover threats that individual tools might miss.


Backed by our 24/7 human-led SOC, you get the visibility and expertise to detect threats earlier, investigate faster, and respond before suspicious activity becomes something much bigger.

4.7/5 average rating
on G2
Read More on G2
4.9/5 average rating
on Capterra
Read More on Capterra

The Warning Signs Are Hiding in Plain Sight

The warning signs of an attack are often hiding in plain sight.

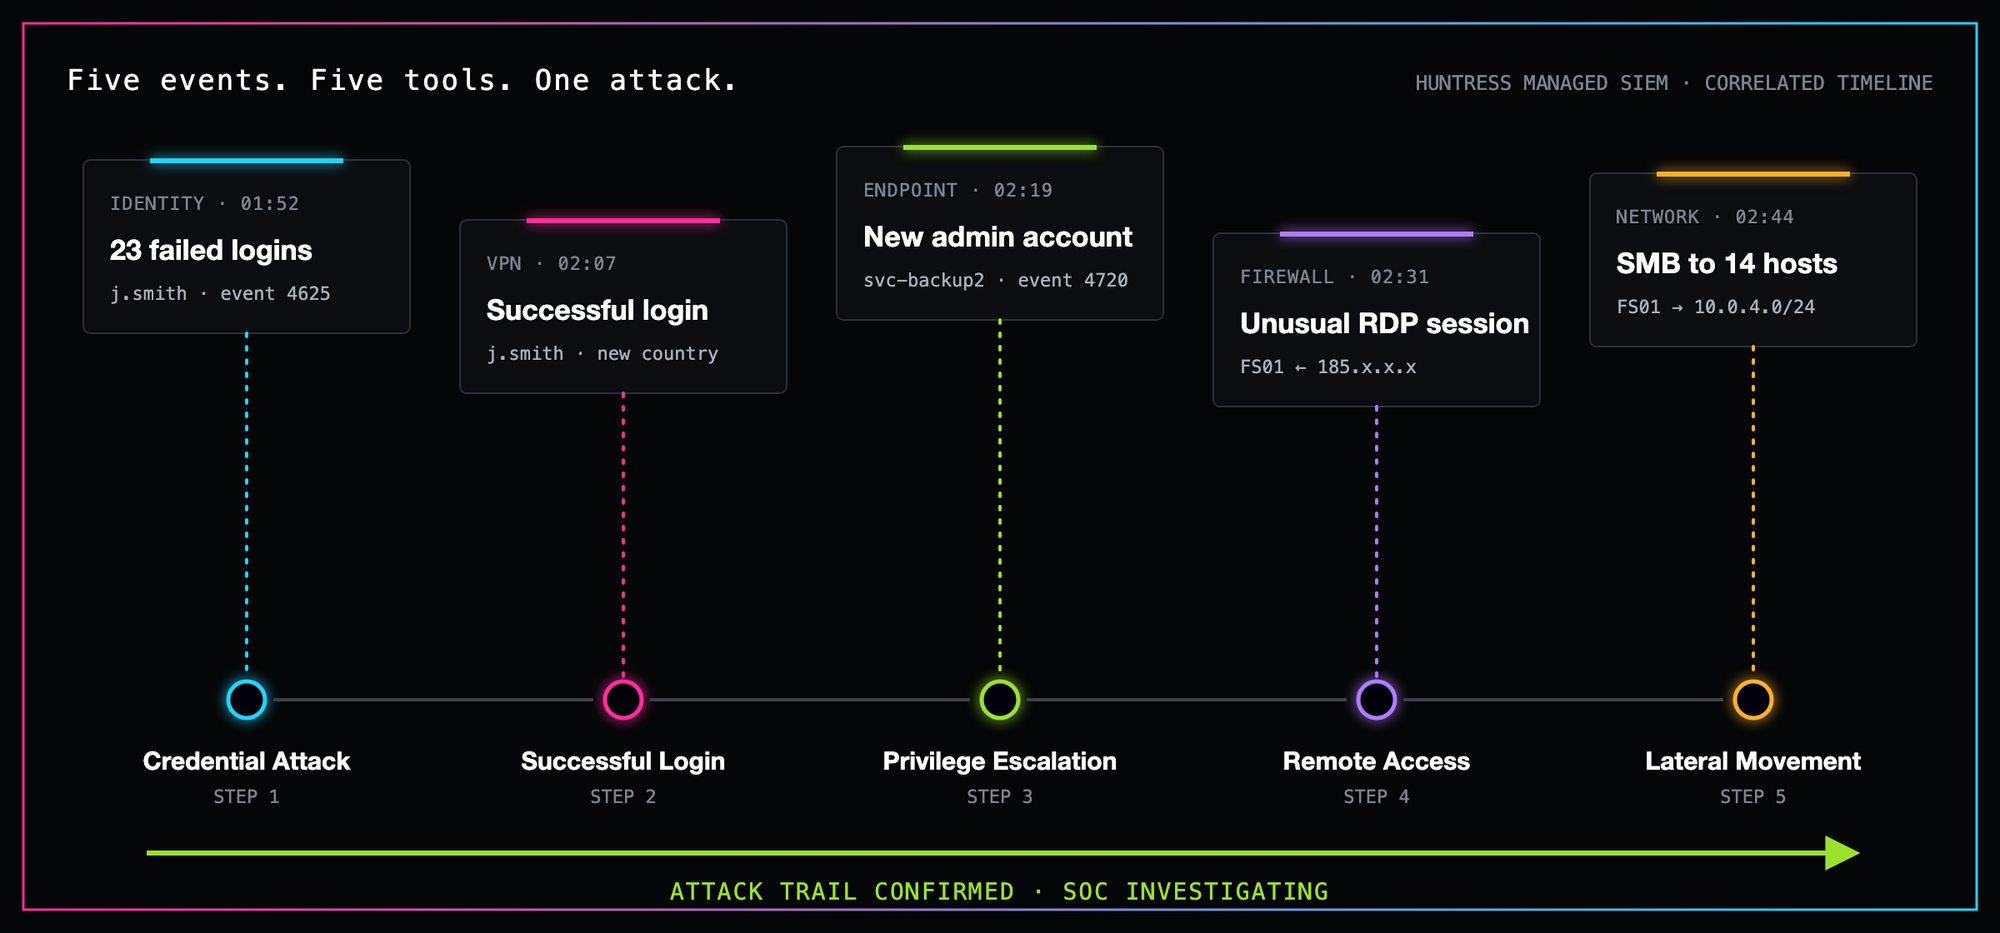
A failed login. A new administrator account. An unusual remote connection. Suspicious activity on a firewall.

Individually, these events might not raise an alarm.

But together? They could reveal an attacker working their way through your environment.

Credential Attack → Successful Login → Privilege Escalation → Remote Access → Lateral Movement

That’s the visibility gap SIEM helps close.

Your security tools are good at protecting what they were built to protect. But attackers don’t limit themselves to one system, one account, or one security product.

Context your SOC can act on.

Huntress Managed SIEM brings security-relevant activity together, giving our SOC the visibility and context to uncover suspicious patterns, investigate connected events, and identify threats that might otherwise go unnoticed.

Attackers don’t operate in silos.

Because attackers don’t operate in silos. Your security shouldn’t either. Huntress connects the dots across your environment, exposing the bigger picture behind seemingly isolated events so threats can be detected earlier, investigated faster, and stopped before attackers can do real damage.

Turn Security Data Into Security Outcomes

Your logs have a story to tell. Huntress helps you find it.

Every login, connection, account change, and security event adds another piece to the puzzle.

The challenge isn’t collecting more information. It’s knowing what matters and what to do about it.

Huntress Managed SIEM turns security-relevant data into the visibility, answers, and actionable insights needed to strengthen your defenses.

Detect Threats Earlier

Catch the warning signs before they become bigger problems.

Attackers leave traces throughout the attack chain. Huntress helps uncover credential attacks, suspicious access, privilege changes, malicious infrastructure, and other behaviors that could signal a threat taking shape.

Connect the Dots Across Your Environment

One suspicious event is a clue. Several could reveal an attack.

Bring together activity from across your environment to understand how seemingly unrelated events connect. See beyond individual tools to investigate suspicious behavior with greater context.

Investigate Faster

When something goes wrong, you need answers. Not another alert.

Search security activity across your environment to reconstruct events, investigate suspicious behavior, and understand the potential scope of an incident.

Quickly answer the questions that matter:

Who logged in?
What system did they access?
What happened next?
Where else did they go?
What changed?
How far did the attack spread?

Huntress gives your team and our SOC the security history needed to reconstruct activity and get to answers faster.

Respond With Confidence

Knowing there’s a threat is only half the battle.

When suspicious activity demands attention, Huntress SOC analysts investigate, separate meaningful threats from false positives, and provide actionable findings to help you take the right next steps.

Less time connecting the dots. More time stopping what matters.

Protection today. Proof when you need it.

A SIEM Is Powerful. A SIEM With a 24/7 SOC Is Something Else.

A SIEM can uncover suspicious activity. But someone still has to do something about it.

That’s where traditional SIEM can become another full-time job.

Someone has to build detections, tune rules, investigate alerts, hunt for emerging threats, and figure out what to do when something is actually malicious.

Huntress handles the heavy lifting.

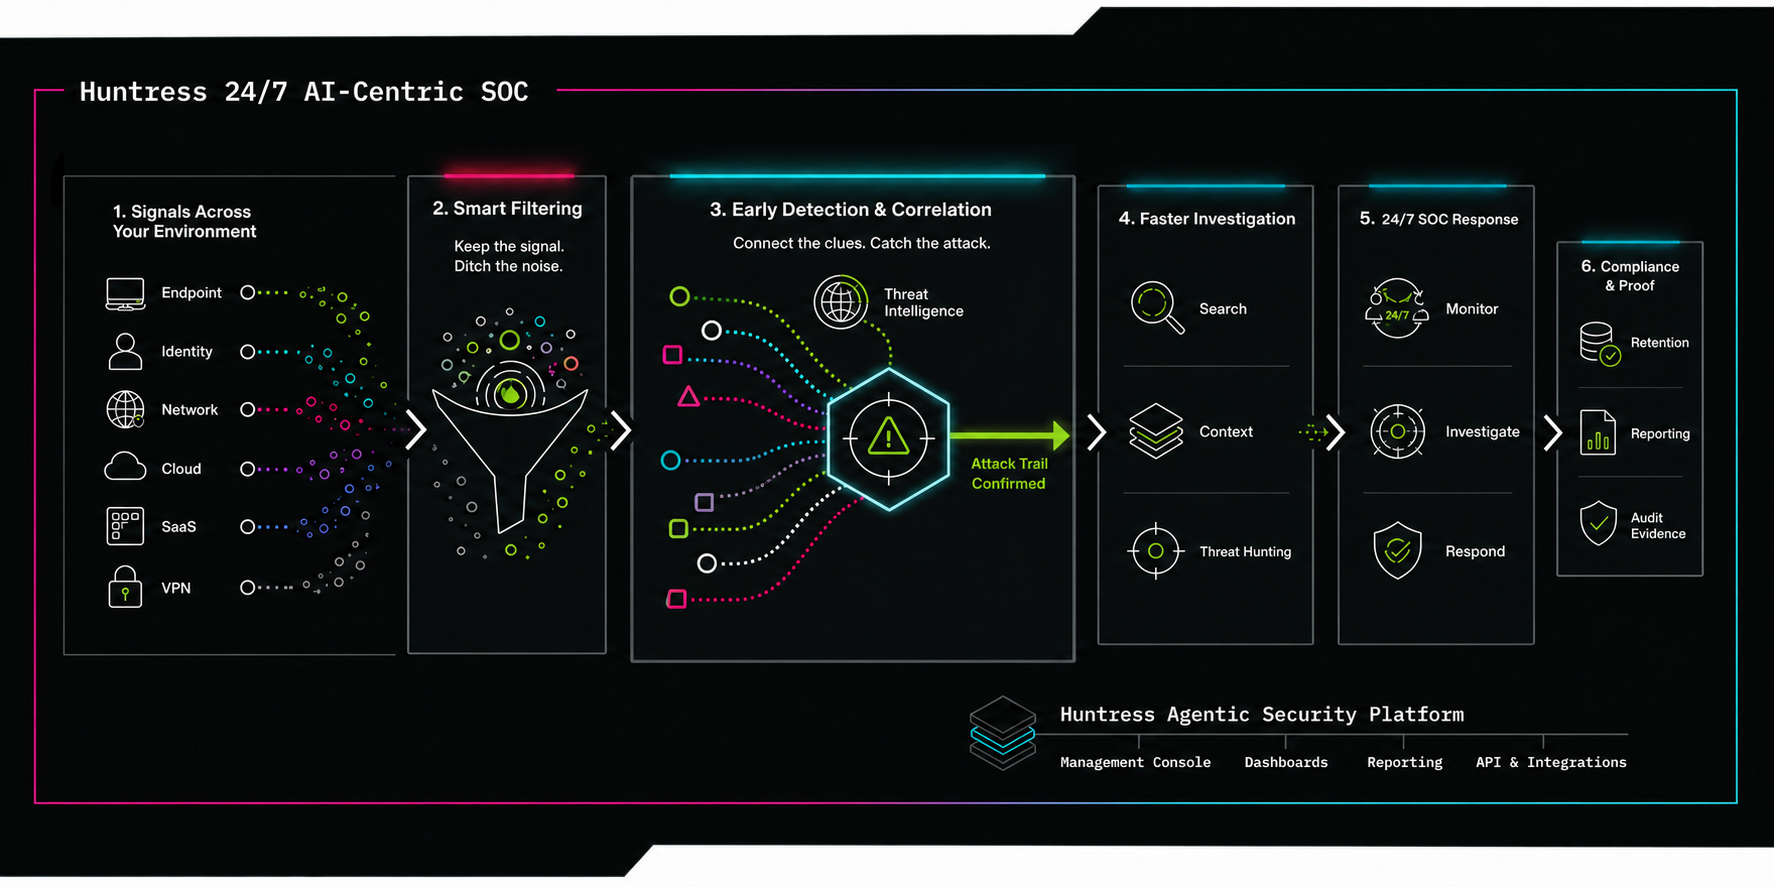
Our 24/7 AI-assisted, human-led SOC combines powerful security technology with real experts who know how attackers operate.

We monitor security telemetry, develop and tune detections, investigate suspicious activity, and help you respond when threats are confirmed.
Always Watching
Always Watching

Threats don’t wait for business hours. Our SOC monitors your security telemetry around the clock, looking for suspicious activity and attacker behavior that deserves a closer look.

Always Hunting
Always Hunting

Attackers change their tactics. We keep hunting. Huntress security experts develop detections, investigate emerging attack techniques, and hunt for evidence of malicious activity across supported security sources.

Always Investigating

Not every alert deserves your attention.

Our analysts investigate suspicious activity, filter out false positives, and provide clear incident findings so your team knows what happened, why it matters, and what comes next.

Ready to Respond
Ready to Respond

When we find a threat, you won’t be left guessing.

Get actionable incident reports, expert remediation guidance, and response assistance to help contain confirmed threats. Where supported, Huntress can take remediation actions on your behalf.

You get the power of SIEM. We do the heavy lifting.

Make Your Existing Security Tools More Powerful

You already have the tools. Let’s put their data to work.

Your security stack generates a tremendous amount of valuable information. But when that information lives in separate dashboards, important connections can be difficult to uncover.

Huntress Managed SIEM brings security-relevant activity from supported tools into one place, giving your team and our SOC a broader view of what’s happening across your environment.

More visibility. More context. More value from the tools you already own. No need to replace your existing security investments to start connecting the dots.

Explore all integrations

Endpoints & Servers
Endpoints & Servers

Collect Windows security events to investigate suspicious system activity, authentication attempts, and important changes across your devices.

Networks & Firewalls

Bring together firewall, VPN, DNS, and network security activity to investigate suspicious connections and potential attacker movement.

Identity & Access
Identity & Access

Gain visibility into authentication events, account activity, and privileged access across supported identity platforms.

Cloud & SaaS
Cloud & SaaS

Extend visibility into supported cloud environments and business applications where attackers may establish access or leave evidence behind.

Keep the Signal. Ditch the Noise.

Your SIEM Shouldn’t Become an Expensive Log Landfill

More logs don’t automatically mean better security.

Traditional SIEM deployments can generate mountains of data, leaving you to figure out what’s actually important while paying to store information you may never use.

Huntress takes a smarter approach.

Our proprietary Smart Filtering identifies and retains security-relevant events while filtering out routine, low-value data that doesn’t meaningfully contribute to threat detection and investigation.

The result?

Less noise. Better signal. More useful security data. Predictable costs.

Your team gets focused information for investigations. Our SOC gets the telemetry it needs to hunt threats. And your SIEM doesn’t become an expensive dumping ground for unnecessary logs.

Because the goal isn’t to collect the most data. It’s to uncover the threats that matter.

Huntress platform

SIEM Search Without Learning Another Language

Ask Your Logs a Question. In English.

Your security data is only valuable if you can actually use it.

Instead of learning ES|QL syntax just to answer a simple question, Huntress AI Search lets you search your SIEM using plain English.

“Show me failed logins from last night.”

“Show me activity from this IP address.”

“Find privileged account changes this week.”

Huntress builds the query for you and returns the relevant logs.

Want to see what happened under the hood? Switch to the ES|QL view to see the translated query, learn from it, modify it, save it, or turn it into a scheduled search.

The power of SIEM without requiring a second language.

Built to Find the Clues Attackers Leave Behind

Threats don’t stay neatly inside one product. Huntress Managed SIEM expands visibility beyond the endpoint to help uncover activity across the broader attack chain.

Credential Attacks
Credential Attacks

Spot patterns like repeated authentication failures and suspicious login activity that can indicate brute force, password spraying, or credential abuse.

Privilege Escalation

Identify important account and permission changes that could give an attacker greater control of an environment.

Suspicious Remote Access

Surface security-relevant VPN, RDP, firewall, and remote access activity that may indicate an attacker establishing or expanding access.

Lateral Movement
Lateral Movement

Connect activity across systems to help identify attackers moving beyond the device or account they originally compromised.

Malicious Infrastructure

Use security telemetry to help identify connections and activity associated with known attacker infrastructure.

Incident Investigation

Search historical activity across security-relevant data sources to understand what happened before, during, and after an incident.

The Biggest Mistakes First-Time SIEM Buyers Make

Don’t buy a Security Information and Event Management (SIEM) solution until you’ve read this guide. Choosing the right SIEM isn’t easy, and one wrong move can leave you with a noisy, overpriced system that doesn’t deliver what you need.

The biggest mistakes first-time SIEM buyers make
Compliance Without Making Compliance the Whole Point

Yes, Huntress Managed SIEM can help you meet demanding compliance requirements.

But we think the security data you’re already collecting should do more than check a box.

Retain security-relevant logs for up to seven years. Search them when you need answers. Build reports when auditors come knocking.

And while they’re sitting there?

Put them to work helping protect your business.

Predictable Pricing. No SIEM Math Degree Required.

Traditional SIEM pricing can punish you for collecting more data, investigating more activity, or simply having a busy month.

Huntress prices Managed SIEM by data source with pooled data allocation, helping reduce unexpected ingestion costs and month-to-month billing spikes.

No guessing what next month’s logs will cost.

No fear of turning on another security source.

No surprise bill because somebody’s firewall got chatty.

Powerful security shouldn’t come with invoice anxiety.

Protecting Businesses Like Yours

We Manage the SIEM. You Get the Outcomes.

You don’t need another dashboard that needs watching.

You need to know someone is watching.

Huntress Managed SIEM combines broad security visibility, Smart Filtering, powerful search, long-term retention, predictable pricing, and the expertise of our 24/7 SOC to turn security data into something far more valuable than storage:

Early warning. Faster answers. Real response.

Huntress platform

Industry-Disrupting SIEM

Managed SIEM Datasheet

Built for the hunt. Priced to protect. Read how Huntress Managed SIEM gets rid of traditional SIEM's complexity, noise, and price tag to deliver threat response and strengthened compliance, fully managed by 24/7 SOC experts at a predictable price.

Frequently Asked Questions on SIEM

Endpoint, identity, firewall, network, and other security products are important because each provides specialized visibility and protection. But attackers don’t limit themselves to one layer of your environment.

SIEM brings security activity from those different systems together, making it possible to identify patterns and investigate behavior across the attack chain.

Think of your individual security products as cameras covering different rooms. SIEM gives you the footage from the whole building. And Huntress gives you the security experts watching it.

Compliance is an important SIEM use case, but it’s only part of the value.

Centralized security telemetry can also help teams detect threats, investigate incidents, hunt for suspicious activity, reconstruct attacker behavior, and respond faster.

With Huntress, the same data retained for compliance can actively support the SOC in protecting your environment.

Huntress combines SIEM technology with a 24/7 human-led AI-centric managed SOC.

Smart Filtering helps retain the security-relevant data that matters instead of blindly storing everything. Huntress SOC experts monitor telemetry, build and tune detections, investigate suspicious behavior, threat hunt, and respond to confirmed threats.

The result is a SIEM built to deliver security outcomes without requiring customers to build and operate their own SIEM program.

Huntress Managed SIEM integrates with the IT and security tools organizations already use, providing centralized visibility across endpoints, network infrastructure, cloud platforms, identity systems, and third-party security controls. Instead of forcing a rip-and-replace, Huntress extends your existing environment by collecting Windows Event Logs from servers and workstations via the Huntress agent, which can also function as a syslog collector for firewalls and network devices. All logs are Smart-Filtered to retain only security-relevant events, securely stored in Huntress’ AWS backend, and made searchable for threat detection, investigations, and compliance reporting.

In addition to core log collection, Huntress Managed SIEM supports third-party endpoint detection and response (EDR) sources from platforms such as CrowdStrike Falcon, Cisco AMP / Secure Endpoint, and SentinelOne, along with identity and authentication integrations including Microsoft 365 and Entra ID (via Huntress Managed ITDR) and Duo. Cloud and infrastructure visibility includes AWS CloudTrail and AWS S3 bucket log collection, as well as DNS and network security platforms like Cisco Umbrella. MSPs and IT teams can also integrate operational tooling such as NinjaOne, with most integrations enabled directly through the Huntress portal using native connectors, APIs, syslog, or an HTTP event collector. Huntress continues to add new integrations over time while maintaining Smart Filtering to control noise, data volume, and costs as environments grow.

Because Managed SIEM relies on Smart Filtering and SOC‑driven triage, you see far fewer raw alerts than you would with a traditional SIEM that ingests everything and forwards every rule hit directly to the customer. Smart Filtering strips out non‑security‑relevant noise at ingestion time, and the Huntress SOC further distills what remains by investigating suspicious events and only escalating incidents that reflect real risk, which significantly reduces false positives and alert fatigue.

When there is a real issue, you see it as an incident in the Huntress portal with a clear explanation of what happened, what data sources were involved, what the likely impact is and what actions have been taken or are recommended.

Yes. Huntress Managed SIEM is designed so MSPs can roll it out quickly and consistently across many clients without a complex project or specialized SIEM expertise. Deployment starts by installing or confirming the presence of the Huntress agent on the Windows servers and workstations you want to monitor; that same lightweight agent is then enabled to collect Windows Event Logs and, where needed, to act as a syslog collector for network devices.

From there, you turn on Windows Event Log collection for selected hosts in the Huntress portal, designate one or more systems as syslog collectors, and point supported firewalls and appliances at those collectors. You can then add cloud and SaaS integrations like Duo, DNSFilter, NinjaOne or SentinelOne through simple configuration in the portal, using native integrations or an HTTP event collector endpoint. MSPs typically start by enabling SIEM on their own environment and a small pilot group of customers, then use the same repeatable pattern and portal‑level configuration controls to scale SIEM across their broader client base in a controlled and predictable way.

Solving the SIEM Problem

Don’t settle for a SIEM that doesn’t work for you. It’s time for a new approach.

Whether you’re grappling with excessive false positives, struggling to find the right expertise, or facing unpredictable costs, you’ll get the insights you need to make informed decisions about your security strategy.

Download the eBook >